
HENNGE K.K. (Headquarters: Shibuya-ku, Tokyo; Representative Director and CEO: Kazuhiro Ogura) announced the release of “HENNGE Mesh Network,” a new addition to its cloud security service “HENNGE One,” available as of October 1, 2026. Leveraging proprietary Peer-to-Peer (P2P) communication technology, this solution fundamentally addresses vulnerabilities inherent in traditional VPNs. It shields devices, such as PCs, from internet-based threats while enabling secure, seamless access to required resources. The service is available through the newly launched HENNGE One plans, including the “HENNGE One Ultra” plan, introduced on the same date.
Recent corporate ransomware attacks frequently exploit vulnerabilities in traditional VPN appliances, underscoring the urgent need to move away from conventional perimeter-based security.
Because traditional VPN gateways are exposed to the public internet, they are prime targets for intrusion; once breached, they allow attackers to move laterally across the internal network (LAN). Moreover, as these appliances have added more features, their growing codebases demand frequent patching and vulnerability management, creating a heavy operational burden for IT teams. Routing all user traffic through centralized gateways also introduces severe latency and performance bottlenecks.
Three Key Features of HENNGE Mesh Network
To address these challenges, HENNGE Mesh Network facilitates a shift from traditional perimeter-based security—protecting access based on location or network—to an identity-driven approach that grants access based on who the user is. This enables organizations to achieve a realistic, effective implementation of Zero Trust.
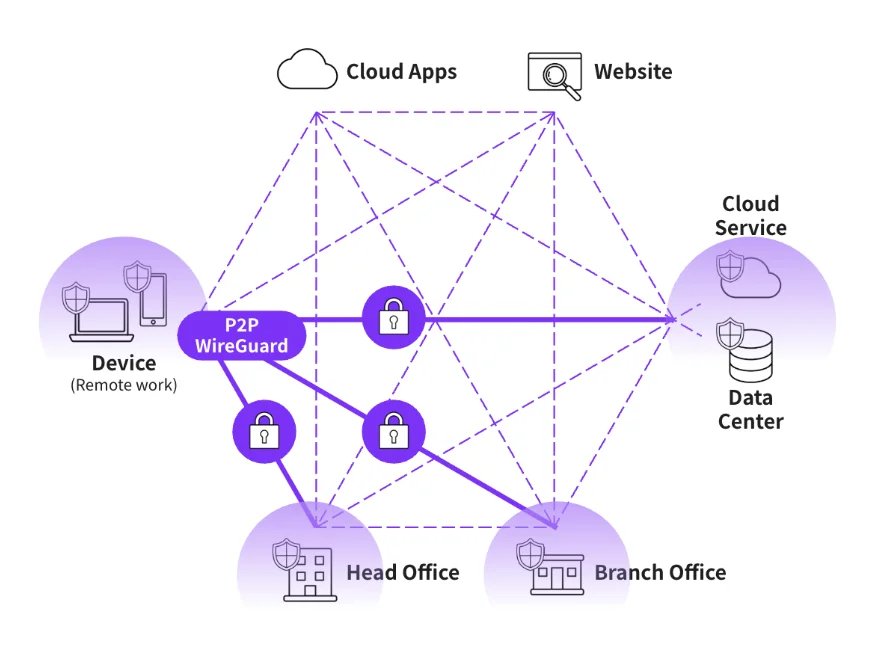
Conceptual Diagram of Device Connectivity via HENNGE Mesh Network
1. Minimizing the Attack Surface
HENNGE Mesh Network eliminates VPN gateway appliances, the primary entry point for external attacks. By establishing direct, encrypted mesh connections between endpoints, it effectively renders internal infrastructure “stealth”—shielding it from internet scans and unauthorized access.
2. Preventing Lateral Movement by Microsegmentation
HENNGE Mesh Network precisely controls communication scope at the software layer without requiring changes to physical router configurations.
- Principle of Least Privilege: Grants access strictly to specific resources required for work, defined on an individual user ID or group basis.
- Damage Minimization: During remote access, even if a single endpoint becomes infected with malware, access control restricts movement to prevent the infection from spreading to other servers or devices.
3. Integrating Seamlessly with HENNGE One Identity Infrastructure (IDaaS)
- Intuitive Web Management Console: Requires no complex network routing design. Administrators can set up and manage access permissions with just a few clicks through the console.
- Instant Automatic Revocation: When an employee leaves or suspicious behavior is detected, simply locking the account in HENNGE Access Control, the identity management component, immediately revokes network access rights.
Three-Step Transition Away from VPNs to Minimize Deployment Risks
Deploying HENNGE Mesh Network does not require immediately shutting down existing VPN appliances. Organizations can start by gaining visibility into vulnerabilities across their publicly exposed IP addresses and VPN ports. Once potential risks are objectively assessed, organizations should clarify baseline requirements—identifying which specific users need access to which servers and ports—to establish least-privilege policies.
A phased migration running in parallel with existing infrastructure follows three steps:
Step 1: Small-Scale Rollout with Selected Teams
Deploy Mesh Network agents on endpoints used by specific teams with frequent remote workers, such as system development departments or IT engineering teams. Organizations can then evaluate deployment effectiveness while running the service in parallel with their existing VPN.
Step 2: Connecting Server Subnets via “Subnet Linker”
Deploy a single relay node (Subnet Linker) within the internal LAN to securely extend P2P access to legacy systems, on-premises file servers, and IoT devices that cannot install the agent directly.
Step 3: Decommissioning Legacy VPNs and Consolidating into the Identity Infrastructure
After confirming access stability and network traffic performance, terminate and physically remove existing VPN appliances to complete the transition to a full Zero Trust environment.
Service Availability & Supported Environments
- Supported OS:
- Client: Windows, macOS, Linux
- Server: Windows Server
- General Availability: October 1, 2026
- Availability Model: HENNGE Mesh Network is offered as an integrated component within the following HENNGE One plans and is not available as a standalone service.
- HENNGE One Ultra (¥2,500 / user / month, excluding tax)
The top-tier suite plan offering access to all HENNGE One services. - HENNGE One IdP Ultra (¥1,000 / user / month, excluding tax)
The flagship identity plan providing comprehensive identity and access management capabilities.
- HENNGE One Ultra (¥2,500 / user / month, excluding tax)
For more details, please visit: (available only in Japanese):
https://hennge.com/jp/service/one/plan2026/
Future Roadmap
HENNGE plans to introduce the following upcoming features and enhancements to HENNGE Mesh Network:
- Expanded Device Support: Extends support for mobile platforms, including iOS and Android.
- App Linker Support: Assigns dedicated static global IP addresses to corporate network traffic, and enables organizations to enforce IP-based access restrictions on SaaS platforms.
- Exit Node Functionality: Securely relays and enforces traffic routing for all internet packets, ensuring safe communication even over untrusted public Wi-Fi networks.
- Device Posture Assessment: Continuously checks and evaluates the compliance and security posture of endpoints, automatically terminating network connectivity if a device falls out of policy.
About HENNGE One
HENNGE One is a cloud security service with the largest market share in Japan* that helps businesses boost productivity. While leveraging new technologies like SaaS is vital for productivity gains, businesses face challenges such as implementing zero-trust security.
To address these challenges, HENNGE One offers three editions: the Identity Edition, which centralizes and protects multiple system IDs for secure and efficient work; the DLP Edition, which prevents accidental leaks of scattered organizational information; and the Cybersecurity Edition, which safeguards companies from cyber-attacks through a comprehensive approach spanning technology, people, and processes.
It achieves zero-trust security through a holistic security service, which reduces the burden of implementation and operation, thereby fulfilling the liberation of technology.
URL: https://hennge.com/global/service/one/
About HENNGE K.K.
Guided by its corporate philosophy, “Liberation of Technology to Change the World,” HENNGE K.K. is dedicated to bridging the gap between advanced technologies and practical application. The company develops and provides two distinctive services: HENNGE One, Japan’s leading cloud security service (*) trusted by over 3 million users, which offers comprehensive security including single sign-on (SSO), access management, email security, secure file sharing, alongside device management and protection based on zero-trust principles; and Customers Mail Cloud, a high-reliability cloud email delivery service.
The company name “HENNGE” combines the Japanese word for transformation, HENNKA, with “CHALLENGE,” reflecting its commitment to embracing change as an opportunity. Established in November 1996, HENNGE listed on the Tokyo Stock Exchange Mothers market (now Growth) in October 2019, and established HENNGE AI in October 2026.
Company name: HENNGE K.K. (securities code: 4475)
Address: Daiwa Shibuya Square, 16-28 Nampeidaicho, Shibuya-ku, Tokyo
Representative: Kazuhiro Ogura (Representative Director, President and CEO)
URL: https://hennge.com/global/
*Ranked No. 1 in the IDaaS Market (Sales and Share by Vendor) for five consecutive years from FY2021 through FY2025 (forecast), based on the ITR Market View: Identity and Access Management/Personal Authentication Cybersecurity Market 2026 by ITR.
– Press Contact
HENNGE K.K.
Corporate Communication Division
Email: hennge-pr@hennge.com
TEL: 03-6415-3660
Person in charge: Ichishima
The names of companies, products, and services mentioned in this press release are trademarks or registered trademarks of HENNGE K.K. or other related organizations.